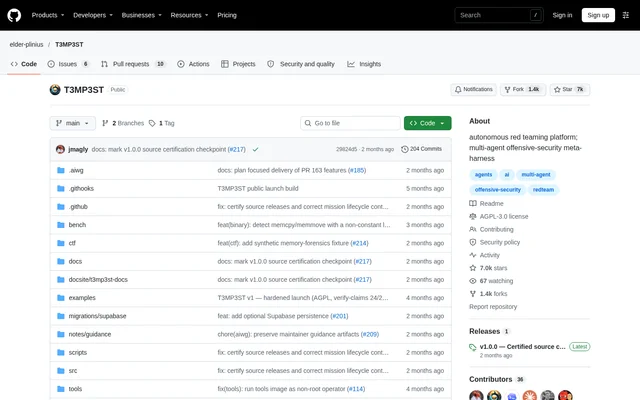
What is T3MP3ST?
T3MP3ST is an open-source, multi-agent offensive-security framework for authorized testing, research, and education. T3MP3ST connects an existing AI coding agent or locally hosted model to a workflow spanning reconnaissance, exploitation, and reporting. Operators can use a browser-based War Room or the CLI to direct assessments of targets they own or have explicit written permission to test.
T3MP3ST describes different levels of readiness across security domains rather than treating every workflow as complete. Web application testing and sandboxed CTF solving are marked stable, while cloud, mobile, and binary capabilities include scaffolding or unbenchmarked components. Source-code analysis supports multi-language ingestion, and the robotics, operational technology, and embedded software disclosure pipeline is marked stable.
What T3MP3ST can do
T3MP3ST combines agent-driven security workflows with interfaces for mission control and local execution. T3MP3ST supports connections to existing coding agents, offline model servers, and optional hosted providers. The repository also documents programmatic access and provides a verification command that recalculates published benchmark claims from committed data.
- T3MP3ST coordinates reconnaissance, exploitation, and reporting for authorized targets.
- T3MP3ST provides browser-based mission control through the War Room.
- T3MP3ST supports hint-free CTF solving inside a sandbox.
- T3MP3ST performs white-box repository analysis with multi-language ingestion.
- T3MP3ST supports offline models through Ollama and OpenAI-compatible servers.
- T3MP3ST documents HTTP API access, library and SDK usage, and MCP setup.
How T3MP3ST works
T3MP3ST starts with a local installation using npm install and npm run server. From the War Room settings, operators connect Claude Code, Codex, Hermes, OpenCode, or Oh My Pi. Operators then describe an authorized target to Op Admiral in plain English and launch a mission, with the connected agent supplying the model-driven reasoning.
T3MP3ST can alternatively use an offline model through Ollama, LM Studio, vLLM, or llama.cpp. Local tool calling is driven through text, so native function-calling support is not required. Docker deployment runs the API server with localhost-only binding, and optional hosted providers offer another route when an operator supplies the relevant API credentials.
Who T3MP3ST is for
T3MP3ST is intended for people conducting authorized security testing, research, and education. T3MP3ST covers web applications, CTF environments, source repositories, and open-source robotics or embedded software, with readiness varying by domain. The repository requires operators to stay within their rules of engagement and obtain explicit written permission before testing systems they do not own.
- T3MP3ST supports external-attacker assessments of authorized web applications.
- T3MP3ST supports sandboxed CTF practice and research.
- T3MP3ST supports white-box analysis of source repositories.
- T3MP3ST supports coordinated-disclosure workflows for open-source vulnerabilities.
T3MP3ST pricing and access
T3MP3ST is available as an open-source GitHub project under the AGPL-3.0 license. T3MP3ST can use an already configured coding agent without new API keys or run fully offline with a local model. Hosted API providers are optional, and the supplied page does not list subscription plans or provider pricing.
T3MP3ST strengths and limitations
T3MP3ST offers self-hosted operation, existing-agent connections, offline model support, and a command for reproducing its published benchmark claims. T3MP3ST also separates stable workflows from incomplete capabilities in its status table. These distinctions matter when selecting an assessment scope, because support for a domain does not mean every exploitation workflow has been benchmarked.
- T3MP3ST has not benchmarked live-cloud exploitation.
- T3MP3ST mobile coverage includes static-detection scaffolding, not benchmarked dynamic exploitation.
- T3MP3ST binary coverage includes static sink detection, not benchmarked solving or exploitation.
- T3MP3ST smart-contract results demonstrate reproduction rather than novel discovery.
- T3MP3ST is provided as-is without warranty.
T3MP3ST FAQ
What is T3MP3ST?
T3MP3ST is an open-source, multi-agent offensive-security framework for authorized testing, research, and education. T3MP3ST uses an existing coding agent or local model to coordinate reconnaissance, exploitation, and reporting through a browser-based War Room or CLI.
Is T3MP3ST free?
T3MP3ST is available as an open-source project under the AGPL-3.0 license. T3MP3ST supports existing coding agents without new API keys and can run fully offline with a local model. Optional hosted providers require their own credentials; the page does not state provider prices.
Can T3MP3ST run offline?
T3MP3ST can run fully offline using a local model. T3MP3ST defaults to Ollama for this workflow and supports OpenAI-compatible servers such as LM Studio, vLLM, and llama.cpp. Local tool calling runs through text rather than requiring native function-calling support.
Which coding agents does T3MP3ST support?
T3MP3ST supports Claude Code, Codex, Hermes, OpenCode, and Oh My Pi as connected local coding agents. Operators connect an agent through War Room settings, describe an authorized target to Op Admiral, and launch a mission using the connected agent.
Does T3MP3ST have an API or MCP support?
T3MP3ST documents an HTTP API, library and SDK usage, and MCP setup. T3MP3ST also supports Docker deployment of its API server, with the documented container configuration binding to localhost rather than exposing the service to the network.
What are T3MP3ST's limitations?
T3MP3ST has unbenchmarked or scaffolded capabilities in cloud, mobile, and binary analysis. T3MP3ST describes smart-contract work as reproduction rather than novel discovery. Authorized use is required, and the project is supplied as-is under AGPL-3.0 without warranty.
From the community
No reviews yet
Be the first to review this tool. What you write helps the next person choose.